
jeffersongoncalves / filament-ccpa-risk-assessments

Filament plugin for laravel-ccpa-risk-assessments: CCPA risk assessments in your panel: score risks, record the reviewers' views, approve, schedule the 3-year review, mark the CPPA submission and find activities still missing one.
Package info
github.com/jeffersongoncalves/filament-ccpa-risk-assessments
pkg:composer/jeffersongoncalves/filament-ccpa-risk-assessments
Requires
- php: ^8.2
- filament/filament: ^5.3
- jeffersongoncalves/filament-plugin-core: ^3.0
- jeffersongoncalves/laravel-ccpa-risk-assessments: ^1.0
- spatie/laravel-package-tools: ^1.16
Requires (Dev)
- jeffersongoncalves/pest-plugin-database-migrations: ^1.0
- larastan/larastan: ^3.0
- laravel/pint: ^1.0
- orchestra/testbench: ^10.0|^11.0
- pestphp/pest: ^3.0|^4.0
- pestphp/pest-plugin-laravel: ^3.0|^4.0
Suggests
None
Provides
None
Conflicts
None
Replaces
None
README
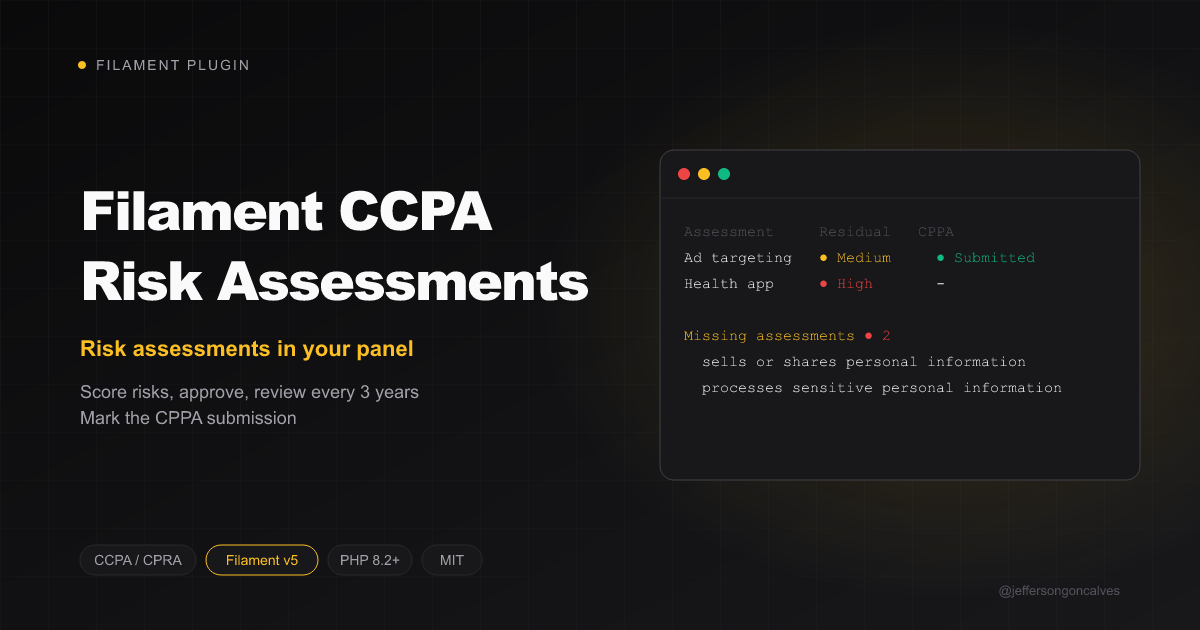
Filament CCPA Risk Assessments
Write the CCPA risk assessments (CCPA Regulations §§7150-7157) of laravel-ccpa-risk-assessments in your Filament panel.
Features
- Assessments linked to a processing activity from laravel-ccpa-notices, with the description of the processing, its necessity and proportionality, and the reviewers' views.
- Risks in a repeater. Each one has an optional LINDDUN threat, a likelihood and an impact from 1 to 3, the measures taken, and the scores after those measures.
- The table shows the highest inherent risk and the highest residual risk (low, medium or high), the status and the next review.
- Approve: asks for the approver's name and schedules the next review. Editing an approved assessment sends it back to draft.
- Missing assessments: lists the processing activities that sell or share personal information, or process sensitive personal information, and have no assessment yet (Regulations §7150(b)).
- Mark as submitted to the CPPA: records the submission of an approved assessment to the California Privacy Protection Agency (Regulations §7157), shown in a column.
- Export (JSON) for each assessment.
- 19 languages.
Compatibility
| Plugin Version | Filament |
|---|---|
| 1.x | 3.x |
| 2.x | 4.x |
| 3.x | 5.x |
Installation
You can install the package via composer:
composer require jeffersongoncalves/filament-ccpa-risk-assessments:"^3.0"
php artisan vendor:publish --tag="ccpa-notices-migrations"   # if not published yet
php artisan vendor:publish --tag="ccpa-risk-assessments-migrations"
php artisan migrate
Usage
use JeffersonGoncalves\Filament\CcpaRiskAssessments\CcpaRiskAssessmentsPlugin;

public function panel(Panel $panel): Panel
{
    return $panel
        ->plugins([
            CcpaRiskAssessmentsPlugin::make()
                ->navigationGroup('CCPA')             // default: no group
                ->navigationSort(7)
                ->navigationIcon('heroicon-o-shield-exclamation')
                ->slug('impact-assessments'),
        ]);
}
All fluent methods are optional. Pair it with filament-ccpa-notices to maintain the processing activities in the same panel.
The resource has no authorization of its own: register it only on panels whose users write the assessments, or add a policy for
JeffersonGoncalves\CcpaRiskAssessments\Models\RiskAssessment.
Testing
composer test
Changelog
Please see CHANGELOG for more information on what has changed recently.
Contributing
Please see CONTRIBUTING for details.
Security Vulnerabilities
Please review our security policy on how to report security vulnerabilities.
Credits
License
The MIT License (MIT). Please see License File for more information.